NSANetwork Security Advisory

Penetration testing for apps and infrastructure.

We assess how applications and APIs enforce access rights and how networks isolate server administration from public services. For each confirmed finding, we explain which privileges an attacker needs, what impact we demonstrated and how to fix the issue.

What we test

From the application to the network.

We select risks and controls with you based on your applications, user roles and network zones. These examples show what an assessment can cover.

Web applications and APIs

We manually check which records users can read or change and which actions their roles permit. We assess workflows covering registration, file uploads, approvals and document signing.

Example: access to another company’s invoice
Servers and systems

We assess exposed services, service account privileges and remote administration settings. When an automated check flags a vulnerability, we verify the installed package version, patch status and configuration of the affected service.

Network infrastructure

We compare the network flows you intend to allow with the services reachable from each agreed segment. For example, an application may need a database connection while its access to the database management interface should be restricted.

The deliverable

What to fix first, and why.

We report technical severity with a CVSS score, its version and scoring vector. Priority depends on where the service is reachable from, the privileges required and the data or operations at risk. The report distinguishes what we observed from consequences that remain hypothetical.

  • Coverage, including versions, user roles and exclusions
  • Technical evidence tied to an environment and an affected component
  • A recommended fix and a clear condition for closing the finding
ILLUSTRATIVE FINDINGAPP–01
Remediation priority: high

A customer could read another company’s invoice

Observation
In the fictional portal, a test user from company A could view company B’s invoice, including the customer name and amount.
Why this takes priority
An ordinary customer account could read another company’s financial data. The example covers two test companies only.
Recommended fix
Check on the server that the invoice belongs to the signed-in company before releasing it. Add an automated check for customer isolation.
Finding classification
OWASP API1:2023 · Broken Object Level Authorization (BOLA)
Closure criteria
An authorized user can view an invoice belonging to their own company. For another company’s invoice, the server denies access and returns no invoice data.
Retest after remediation Pending verification

Engagement

From scope to retest

  1. Agree the scope and operating limits

    Before we start, we need your written authorization specifying the scope, dates and permitted roles. The system owner or an authorized representative must grant it. For web applications, we select checks from the OWASP Web Security Testing Guide (WSTG) that match the features in scope. For production work, we agree a testing window, operational limits and a contact who can stop the assessment.

  2. Establish the impact within scope

    For each finding, we document the affected component, the starting privileges and the observed result. If an issue needs immediate action, we notify the designated contact during the assessment.

  3. Review the findings and verify fixes

    Your team reviews the findings and supporting evidence for factual accuracy before we finalize the report. The scope can include one retest after remediation. For each finding we reassess, we record the system version, date and outcome. You can also arrange periodic checks of selected functions or a review after a significant system change.

Who performs the tests

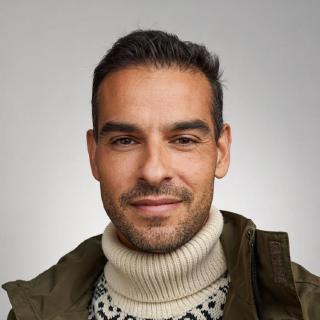
Martin Růžek

Martin Růžek conducts the tests. He is the managing director of NOVERIA networks s.r.o. and has more than 20 years of experience in IT.

If NOVERIA is involved in developing or operating your system, we will tell you before the contract is signed.

Contact

Request a penetration test

Tell us which systems you want assessed, the objective and any operating constraints. We will reply by email to discuss the scope.

You can also use this form to report a security issue on NSA.cz.

Please keep credentials and other sensitive information out of your enquiry.

NOVERIA networks s.r.o. is the data controller. We use your details only to respond to your submission. If an enquiry does not lead to a contract, we delete it and the related email correspondence six months after the last contact.